A macOS information-stealing malware can hijack Telegram Desktop sessions and compromise cryptocurrency wallets, according to blockchain security firm SlowMist.
The malware harvests data from the macOS Keychain, Safari cookies, Apple Notes, Telegram Desktop and databases associated with more than a dozen cryptocurrency wallets.
After collecting passwords and authenticated sessions, the malware copies users’ authenticated Telegram Desktop session data, wallet databases and browser wallet extension data.
SlowMist said attackers can then attempt to decrypt the stolen wallet databases offline using passwords harvested from the infected device or replace legitimate Ledger and Trezor applications with fake versions that trick users into entering their recovery phrases. The security firm reproduced the attack chain in an isolated environment.
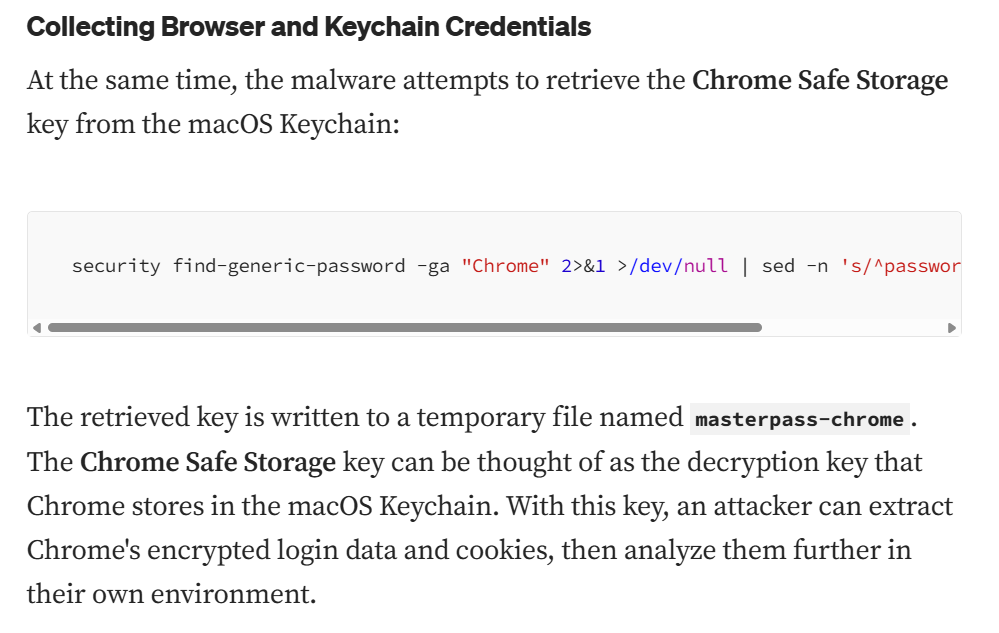
MacOS malware code used to steal keys and passwords. Source: SlowMist
Related: AI has not triggered DeFi ‘hackpocalypse,’ Dragonfly partner says
MacOS malware targets popular crypto wallets
According to SlowMist, the malware combines multiple techniques into a coordinated attack chain, allowing attackers to pursue different methods of compromising cryptocurrency accounts and wallets.
The malware targets software wallets including Exodus, Atomic, Electrum, Wasabi and Monero, as well as hardware wallet applications such as Ledger Live and Trezor Suite, according to SlowMist. It also searches for wallet data stored by full-node clients including Bitcoin Core, Litecoin Core, Dash Core and Dogecoin Core.
Telegram two-step verification does not prevent the attack because the malware reuses an authenticated local session instead of creating a new login, according to SlowMist. In tests, researchers restored stolen Telegram Desktop session data on another Mac without entering a phone number, verification code or two-step verification password.
SlowMist urged users who suspect their devices have been compromised to immediately terminate existing Telegram sessions, establish a new trusted login and change both their Telegram two-step verification password and Telegram Desktop Passcode. The company also recommended generating a new recovery phrase on a clean device and transferring all assets to new addresses.
Magazine: Does Botanix’s failure prove Bitcoiners don’t care about DeFi?