The Binance attacker spent at least 36 hours preparing for the $6.36 billion crypto exchange hack that began with $296 million in XRP.
According to an Oct. 29 investigation by TRM Labs, the attacker began preparing the operation on Oct. 28 before executing coordinated transfers across 10 blockchains the following evening.
The blockchain intelligence firm found that most of the funds left Binance-linked wallets within approximately 20 minutes, making the incident the largest cryptocurrency theft on record.
How the Binance attack unfolded across 10 blockchains
TRM traced the earliest preparations to the morning of Oct. 28, when an attacker-controlled wallet received three small transfers from Tornado Cash, a cryptocurrency mixing service.
Early the following day, the attacker deployed malicious smart-contract code and tested it against two newly created Ethereum wallets.
The attacker subsequently deployed a revised version and rehearsed the operation on a third wallet, successfully transferring test funds before returning them.
Approximately four hours after that final rehearsal, the main attack began.
Between 20:05 and 20:09 UTC, five Binance wallets on the XRP Ledger transferred approximately 233.46 million XRP, valued at $296 million, into a single attacker-controlled address.
On-chain investigator Wazz Crypto reached a similar conclusion, saying:
“This was actually the canary in the coal mine as the Ripple hack [sic] apparently started 10 mins before all the other chains.”
By 20:10 UTC, suspicious transfers had also begun from Binance wallets on Solana and Optimism.
At 20:20 UTC, a Binance Bitcoin wallet transferred 18,270 BTC worth approximately $1.47 billion. The attacker immediately began splitting the funds into smaller batches of 1,000 BTC and 100 BTC.
Within two minutes, a Binance wallet on Tron transferred another 612.7 million USDT and 46.4 million TRX, worth approximately $628 million combined.
The Ethereum operation unfolded almost simultaneously.
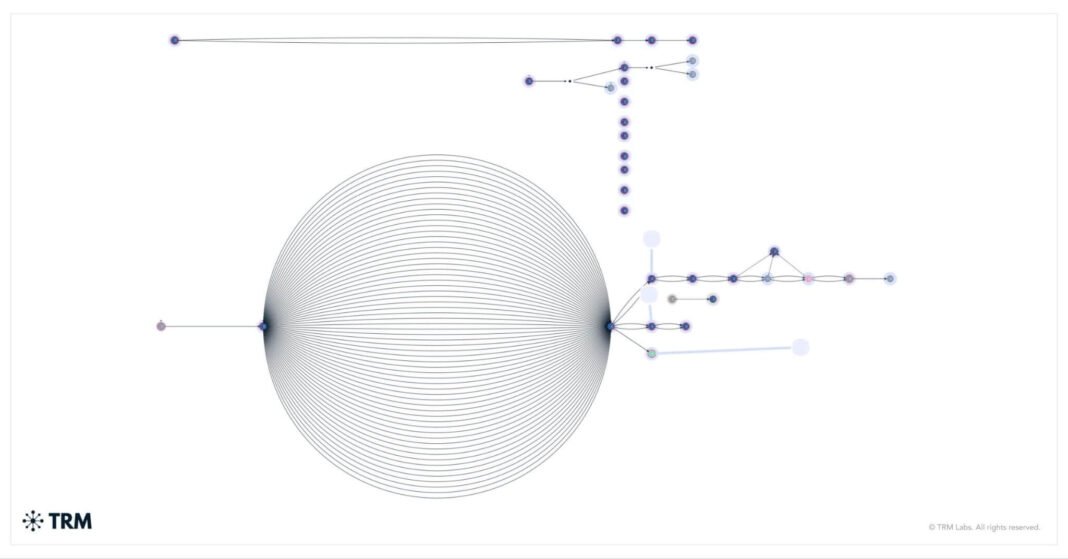
At 20:20 UTC, the attacker submitted 50 previously signed EIP-7702 authorizations to a Binance hot wallet, allowing it to delegate execution to a malicious smart contract.
The authorizations covered consecutive transaction counts, ensuring that one would match the wallet’s current count when processed.
Three minutes and 24 seconds later, the attacker activated the contract’s sweeping function, transferring 167,464 ETH and 63 tokens, including 1.615 billion USDT, in a single transaction.
The attacker subsequently executed additional sweeps at 20:41, 20:59, 21:04, 21:44, 22:39 and 23:56 UTC as more assets entered the compromised wallet.
The delegated wallet also exercised its existing permissions over a separate Binance smart account, facilitating the transfer of another 823 million USDC.
A second wave around 23:05 UTC extended the operation to additional Binance wallets on Avalanche and Polygon.
By 00:30 UTC on Oct. 30, TRM had traced approximately $6.36 billion in transfers across Ethereum, Bitcoin, Tron, the XRP Ledger, Solana, Arbitrum, Optimism, Base, Avalanche and Polygon.
While investigators have reconstructed the sequence, the source of the necessary authorizations that allowed the attack remains unresolved.
Ethlabs researcher Derek Chiang said the attacker could have obtained the wallet’s private key or tricked its owner into signing a malicious authorization. He also emphasized that the attacker needed valid authorization to execute the EIP-7702 operation.